RISK 01
Access has grown over time
Permissions, service accounts, and external access are broader or more permanent than necessary.
Security you can demonstrate
For SaaS and software companies preparing for audits and enterprise deals
Enterprise customers and auditors ask for more than policies. They want to see how access, changes, data, and incidents are controlled in practice. We make gaps visible before they surface in the wrong conversation.
30 minutes · directly with Niels · no sales script
8+
years of infrastructure experience
12x
AWS certified
Golden
CNCF Kubestronaut
Direct
access to the expert doing the work
Does this sound familiar?
Many teams have sensible security measures in place. Problems arise when controls are inconsistent or gathering evidence requires too much manual work.
RISK 01
Permissions, service accounts, and external access are broader or more permanent than necessary.
RISK 02
Logs, configurations, and responsibilities have to be gathered from scratch for every request.
RISK 03
Long checklists show many possible measures, but not which risks threaten deals or operations first.
After the engagement
The deep-dive combines technical assessment with your specific certification or customer context. The result is a realistic order of work instead of an endless wish list.
Findings are documented clearly and ranked by risk.
Missing technical evidence and recurring manual work are identified specifically.
Actions include an objective, priority, and realistic implementation path.
What you receive
How it works
01
STEP 01
We clarify the objective, environment, and current pressure to act. You then know whether the assessment is genuinely a fit.
02
STEP 02
I review documentation, configuration, and data and speak with the people responsible for the environment.
03
STEP 03
In the readout, we prioritize findings, effort, and next steps together according to business impact.
This is a fit if ...
This is not a fit if ...
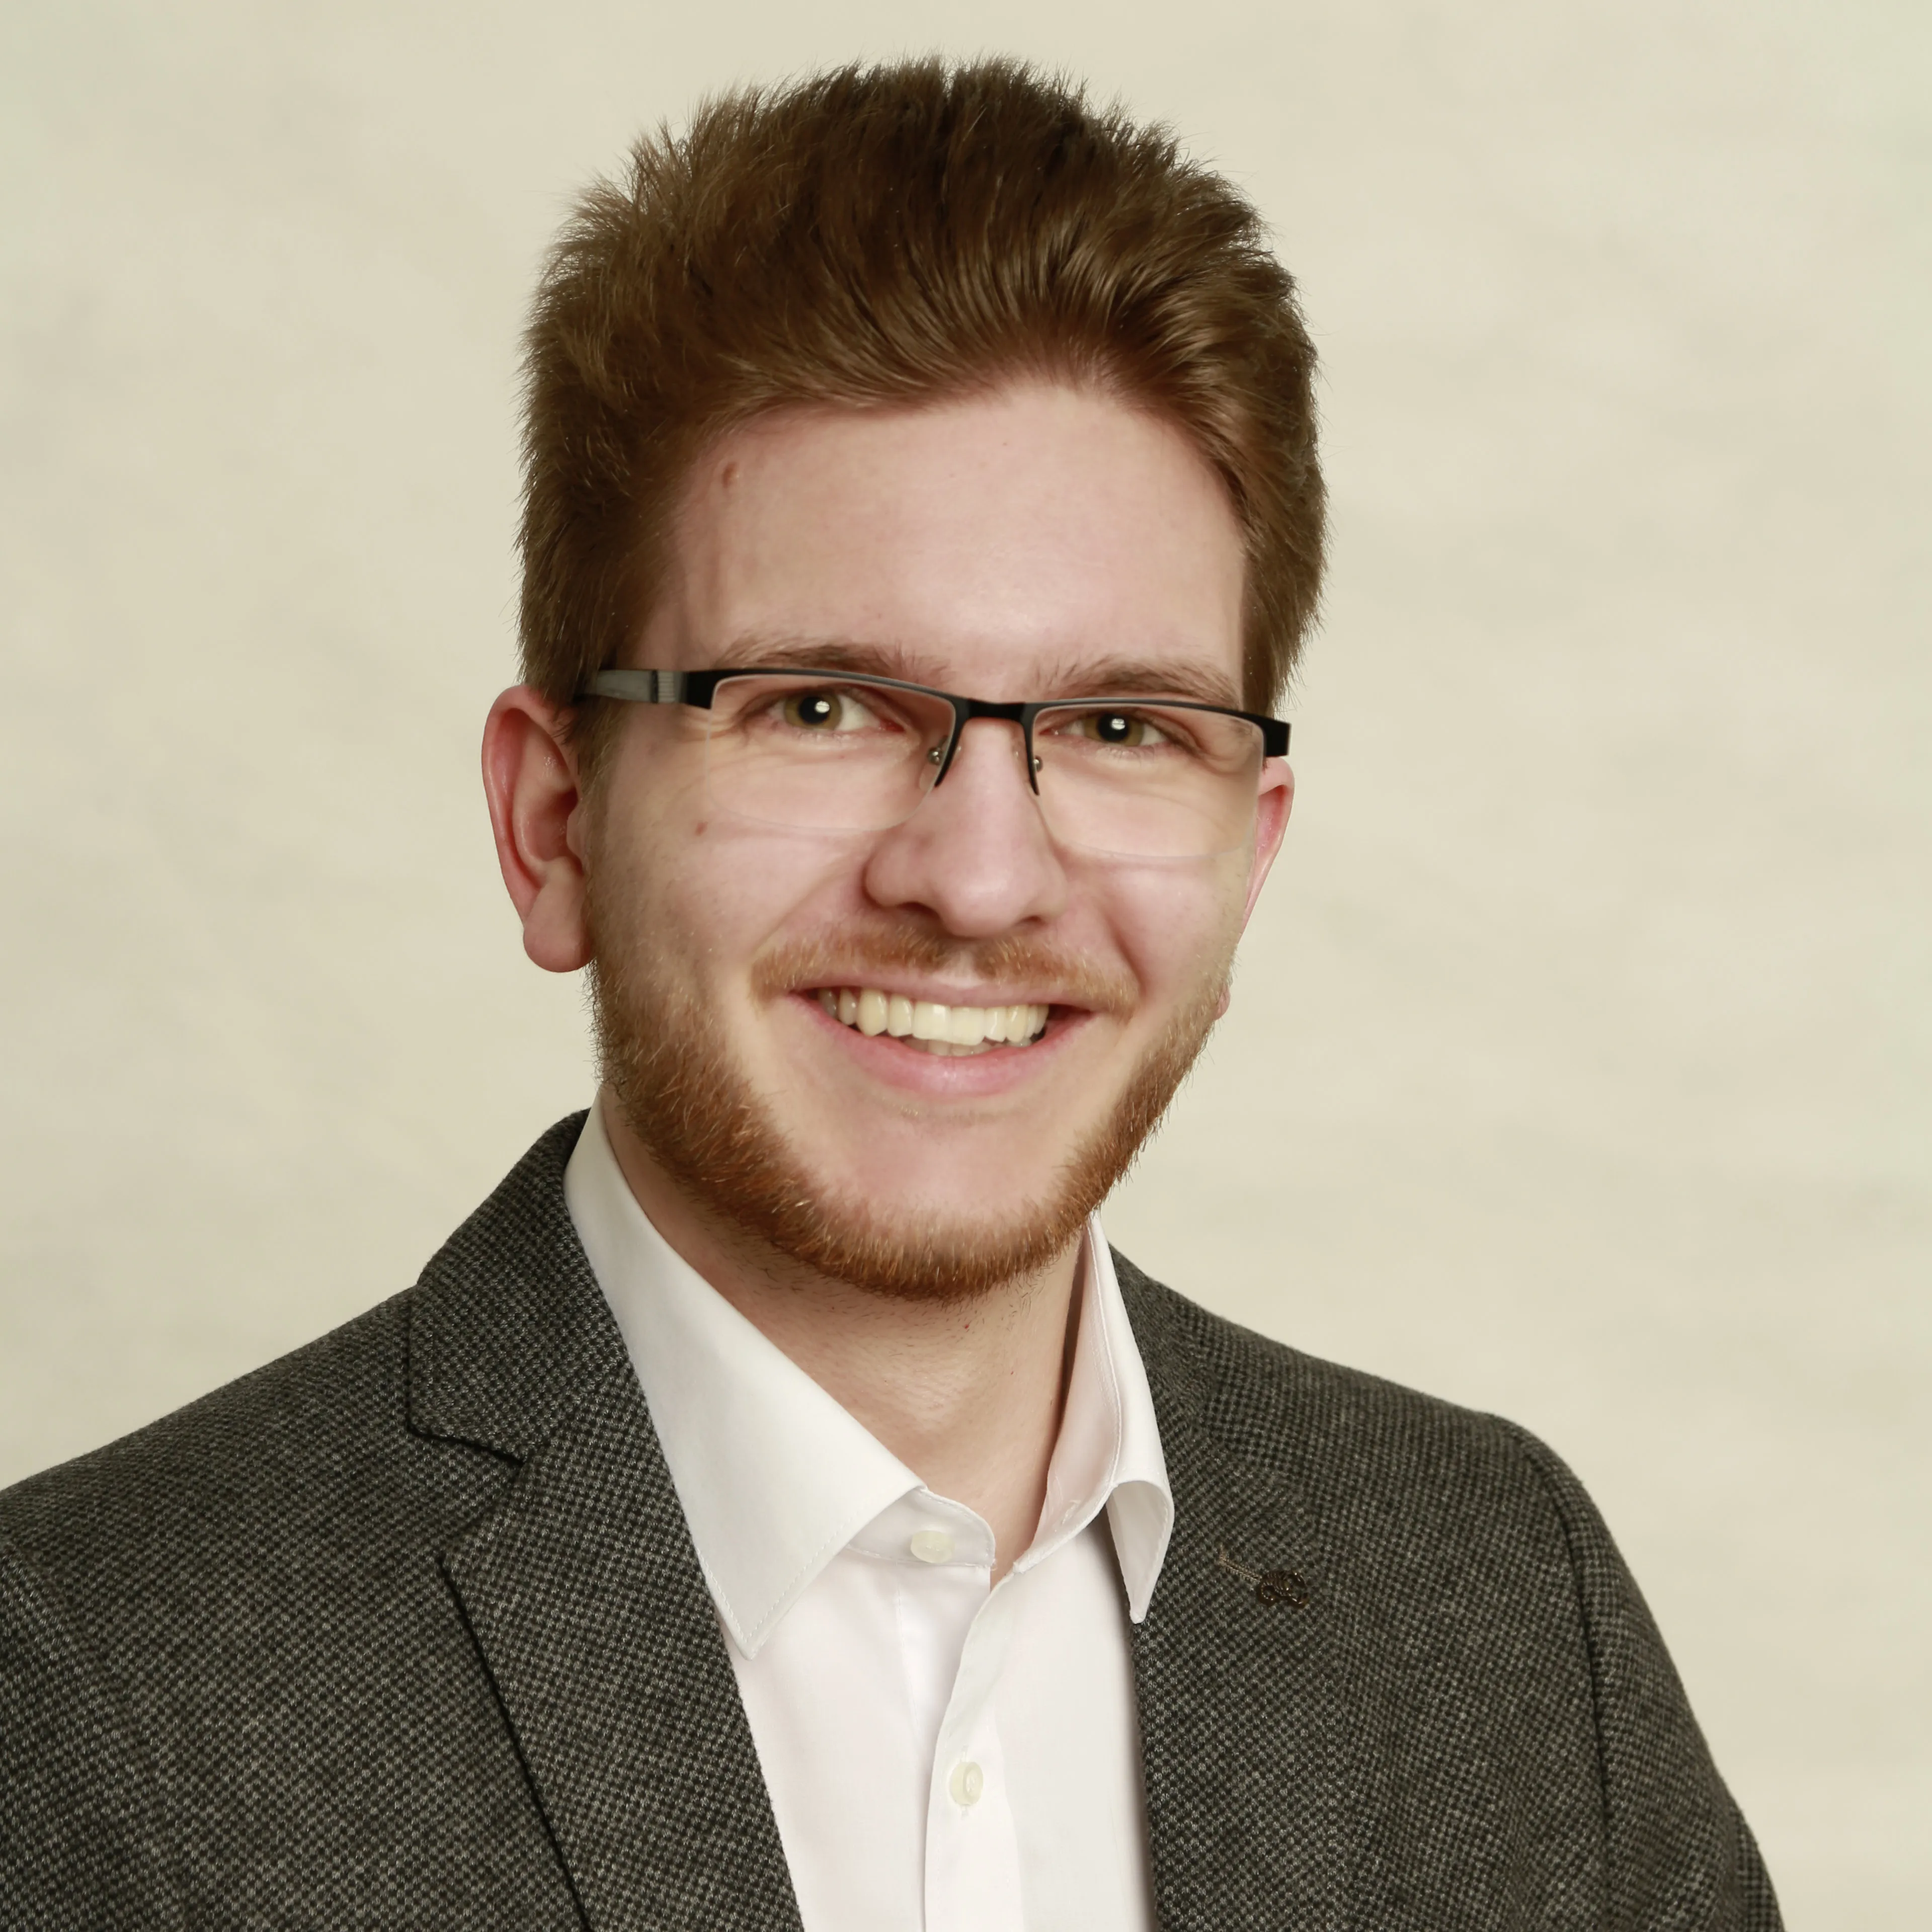
You work directly with Niels
I am Niels Heidbrink. For more than eight years, I have built and operated cloud infrastructure for SaaS companies, software vendors and e-commerce, on AWS, Azure, IONOS and Hetzner. I hold 12 AWS certifications and the CNCF Golden Kubestronaut title.
“Niels works in an extremely structured, efficient, and solution-oriented way. He thinks beyond the immediate task, understands connections quickly, and implements requirements pragmatically and reliably.”
Frequently asked questions
No. I assess technical controls and evidence in your infrastructure. Legal advice, the management system, and official certification remain with the appropriately qualified parties.
Yes. Existing requirements, findings, and evidence formats can inform the scope of the technical assessment.
Access is kept to a minimum and limited in time. Before we begin, we agree on binding arrangements for reporting, storage, and deletion of sensitive information.
The next step
In a free 30-minute call, we discuss your situation. If this assessment is not the right next step, I will tell you openly.
Book a free fit checkNo preparation required · no obligation
More entry engagements
EU cloud instead of US cloud
For B2B SaaS companies in Germany, Austria and Switzerland with 10 to 100 employees, running on AWS, Azure or Google Cloud
Out of the US cloud, into an EU cloud: an EU cloud check in two weeks, the migration in 8 to 12 weeks with a way back, then operations with evening maintenance. Everything is yours as code.
See scope & processFewer exceptions. Safer releases.
For software vendors and ISVs with a growing number of customer environments
Find out which standards for customer environments and deployments save you the most work, so new releases and projects do not start from scratch every time.
See scope & processKubernetes under control
For B2B SaaS companies running production workloads on Kubernetes
Identify operational, security, and cost risks in your Kubernetes platform and receive a prioritized action plan.
See scope & process© 2026 dthn Technology Estonia OÜ
contact@dthn.io | +372 5898 9763
Registry code: 17157148 | VAT ID: EE102917729